Versionix
Dependency analytics to plan upgrades without surprises.
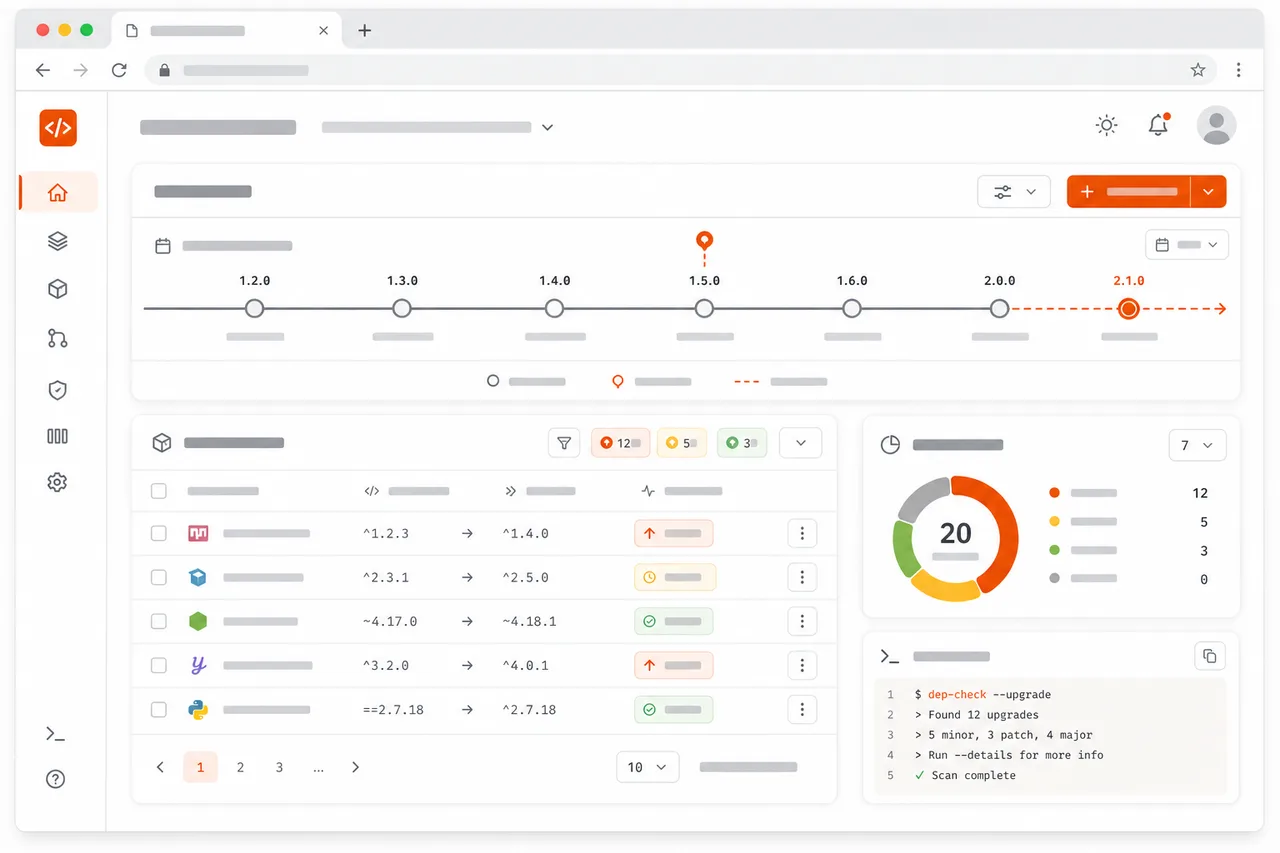
Upgrading dependencies is a gamble when you don't know the real risk
Between outdated versions, changelogs nobody reads in full, and breaking changes that only show up in production, keeping dependencies current becomes a task teams keep postponing.
- Dozens of outdated dependencies with no clear visibility into which ones are urgent.
- Breaking changes discovered after upgrading, not before.
- Long, technical changelogs nobody has time to read in full.
- Upgrade decisions that depend on one team member's memory.
Connect your project
Versionix reads your dependency manifests (package.json, requirements.txt, and more) automatically.
Analyze the risk
Every outdated dependency gets a risk score based on breaking changes, security and project activity.
Plan the upgrade
Get a suggested upgrade order, grouping safe changes first.
Verify before merging
Integrate Versionix into your CI to automatically flag when a new version introduces risk.
Outdated version detection
See at a glance which dependencies are behind and by how much, across all your projects.
Per-upgrade risk score
Every update is evaluated by likelihood of breaking changes, not just version number.
Changelog summaries
Get a clear summary of what actually changed between your current version and the available one.
Migration planning
Order large upgrades into safe steps, with interdependencies resolved automatically.
Security alerts
Find out first when a dependency you use has a recently disclosed vulnerability.
Dependency health dashboard
Track your project's dependency technical debt over time.
Coming soon
Plans and pricing for this product will be announced soon.