Fissurix
Vulnerability scanning for code, dependencies, Docker and Git, in one place.
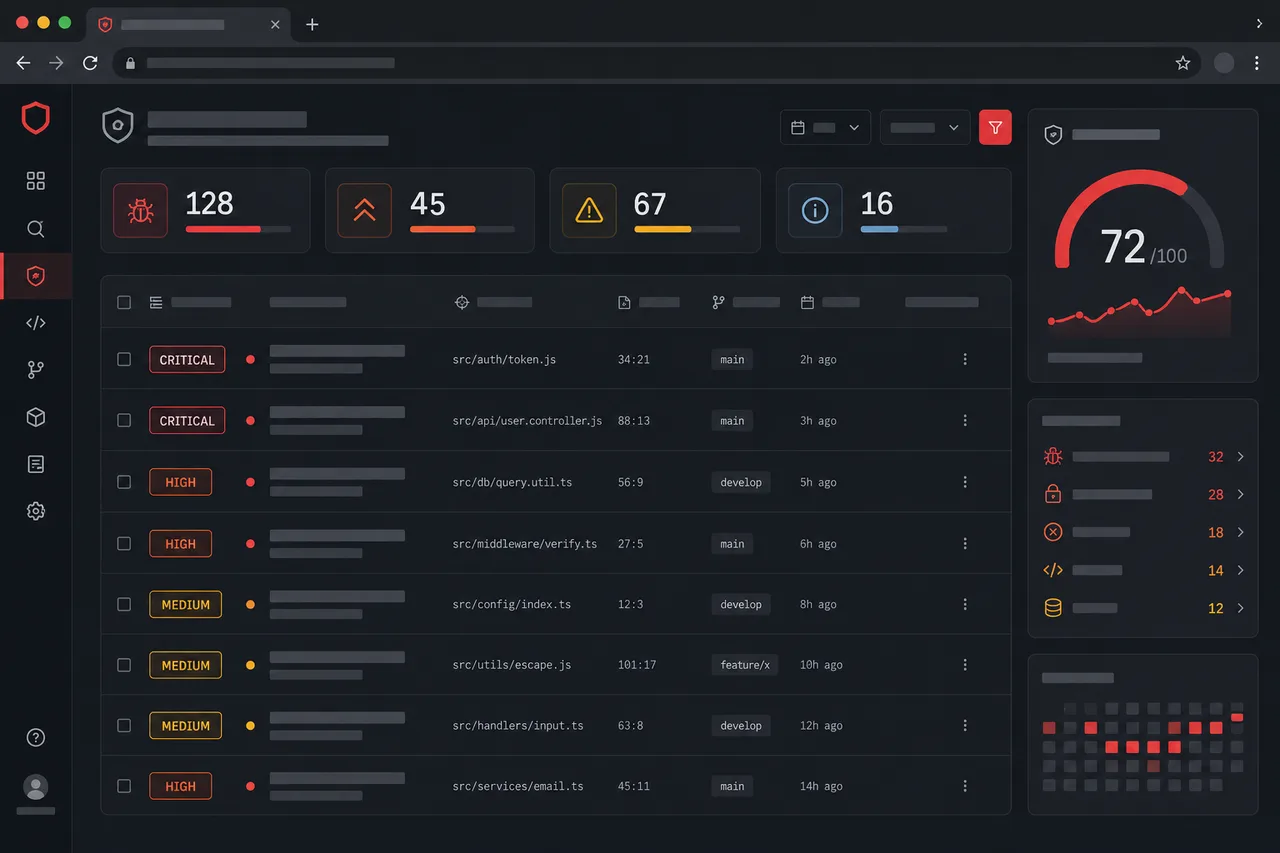
Vulnerabilities hide in more places than a single scanner covers
Your own code, third-party libraries, Docker images, and even secrets forgotten in Git history: every layer needs its own tool, and coordinating them by hand doesn't scale.
- Outdated dependencies with known CVEs that nobody reviews until it's too late.
- Docker images built on top of base layers with unpatched vulnerabilities.
- Secrets and credentials that got committed at some point in Git history.
- Security reports scattered across several tools, with no unified view of risk.
Connect your repository
Integrate Fissurix with GitHub, GitLab or Bitbucket in minutes, without changing your workflow.
Multi-layer scanning
Fissurix analyzes source code, dependencies, Docker images and Git history on every push or on a schedule.
Prioritize by real risk
Every finding is ranked by severity and exploitability, so your team focuses effort where it matters.
Integrate with your CI/CD
Block merges with critical vulnerabilities and get alerts straight in Slack or the channel you use.
Source code scanning
Catch insecure patterns and known vulnerabilities directly in your code, without leaving the repo.
Dependency analysis
Identify libraries with known CVEs and get suggested safe versions to upgrade to.
Docker image scanning
Analyze your image layers for vulnerabilities in the base system and installed packages.
Git history
Find secrets, tokens and exposed credentials anywhere in your commit history.
CI/CD integration
Add Fissurix as a security gate in your pipeline, with configurable rules by severity.
Unified risk dashboard
See the security status of all your repos in a single dashboard, with trends over time.
Coming soon
Plans and pricing for this product will be announced soon.